01 A little introduction

Hi, I’m
Boss.

Rujikorn Ngoensaard

Senior Data Engineer

I build and operate
enterprise data platforms.

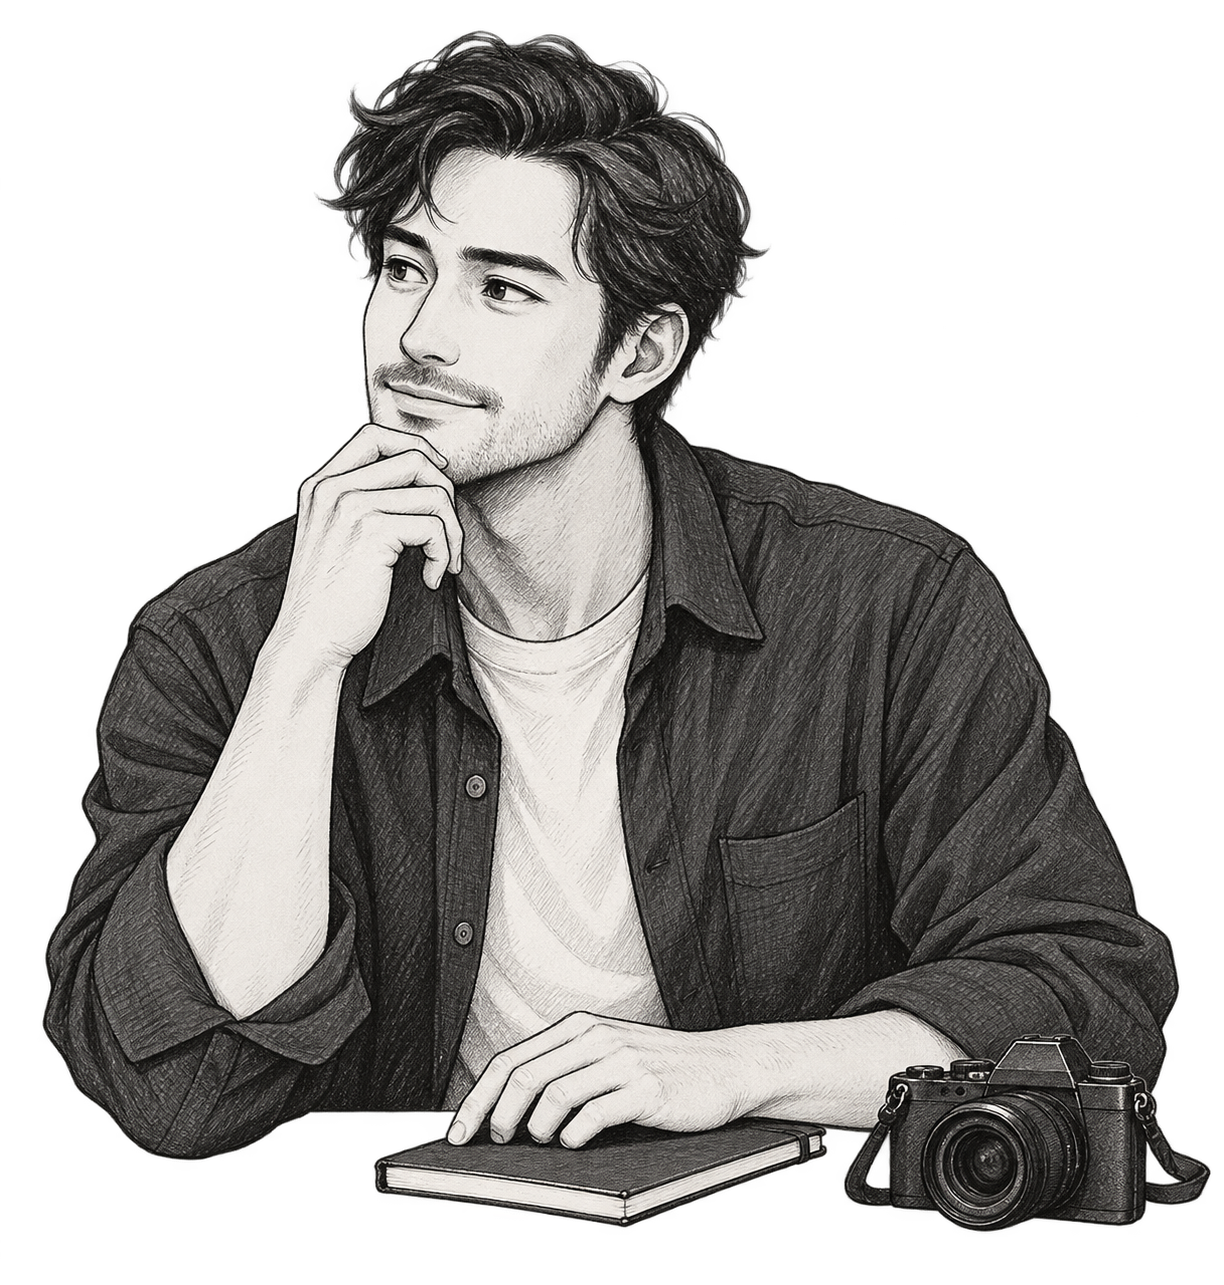
An original ink illustration of Boss, looking thoughtful beside a camera and notebook.

Where I started

Bachelor’s in Electrical and Electronic Engineering,
Ubon Ratchathani University, 2013–2017.

Outside of work

  • Photography
  • Collecting
  • Exploring new tech

02 The journey

From engineering
to data platforms.

An evolving practice across manufacturing, commerce and enterprise data.

2013–2017 · The foundation

Electrical and Electronic Engineering

Ubon Ratchathani University

  1. Nov 2017–May 2020

    Seagate Technology

    Process Engineer, Engineer I

    Developed diagnostic and repair-routing automation for HDD testing. Operated scripts across 130+ Linux VMs and coordinated technical repair and retest work.

  2. May 2020–Dec 2021

    Western Digital

    Product Design Engineer

    Promoted from Senior to Staff Engineer

    Automated reporting and centralized data workflows with Airflow. Redesigned ML prediction services for HDD testers.

  3. Jan 2022–Jan 2023

    NocNoc / Betterbe Marketplace

    Data Engineer

    Built personalization pipelines, search and product-discovery services. Selected website placements recorded more than 50% relative improvement in click-through rate.

  4. Feb 2023–Jul 2024

    The1 Central

    Data Engineering Specialist

    Delivered AWS lakehouse pipelines for 150+ sources within assigned domains. Built governance foundations and enabled experiment tracking through a private MLflow deployment.

  5. Oct 2024–Present

    Central Pattana

    Senior Data Engineer

    Build and operate enterprise data platforms across integration, analytics, governance and production support. Lead technical delivery with three outsourced engineers and design target architecture with infrastructure and security stakeholders.

A closer look at my work

03 Selected work

Engineering at
Central Pattana.

Senior Data Engineer
October 2024–Present

I build and operate enterprise data platforms and lead technical delivery with three outsourced engineers.

Additional engineering work

Enterprise Integration

Build and validate enterprise ingestion with ADF, Databricks and ADLS.

Standards & Governance

Developed naming, ownership and access standards; adoption continues.

Platform Operations

Investigate platform constraints and coordinate incidents, capacity decisions and vendor follow-up.

Analytics Migration Central Pattana

Tracing a path through missing lineage.

Result

Project delivered in three months:

Datasets
200+
Reports
100+
Users
1,000+

Objective

Move Tableau analytics to Microsoft Fabric and Power BI.

Challenge

Missing dictionaries, specifications and source ownership required dashboard-to-source lineage reconstruction.

My role & scope

I led technical delivery and coordinated data engineering with the project team.

What I did

  • I traced dashboard-to-source dependencies.
  • I coordinated ingestion with Infrastructure and existing Airflow workflows under compute and scheduling constraints.
  • I established batch checks and same-period report validation.
Tableau Microsoft Fabric
& Power BI
Engineering details

Validating each incoming batch

Direct source-database access was restricted for this migration. Source delivery used data files plus accompanying metadata files for file-level validation.

Source delivery

  • Data files
  • Accompanying metadata files

ADF

Does the batch contain records?

Zero records Skip

Skip all remaining downstream tasks for that batch.

Nonempty batch Databricks

Check row counts and columns against the accompanying metadata.

Report acceptance

Power BI results must match the equivalent Tableau report for the same reporting period.

RLS Automation Central Pattana

Automating the routine, keeping business control.

Result

Rolled out July 2026: daily processing and 12 domain workbooks.

Objective

Replace person-operated refresh, extraction and Excel macros with scheduled daily processing.

Challenge

Preserve established access decisions and downstream compatibility.

My role & scope

I owned engineering for the master RLS pipeline and dashboard distribution.

What I did

  • I built scheduled ADF and Databricks processing.
  • I kept access decisions with business owners while automating routine execution.
  • I generated compatible workbooks and Fabric datasets.

Organisation data + prior approvals

Scheduled ADF/Databricks processing

Workbooks + Fabric datasets

New groups

Business decisions

Reviewed assignments feed a later run

Engineering details

Assignments and business review

Current organisation data identifies who exists; approved assignments and business review determine access. Regular users can inherit their existing organisation group’s approved assignment.

  1. Use a nonblank business-reviewed assignment.
  2. Otherwise retain the prior approved assignment.
  3. Otherwise apply effective access of No.

A reviewed No is a decision; blank is not approval. Groups absent from the approved baseline enter the review queue with blank review fields and effective access of No while unresolved. Daily processing continues with outstanding reviews.

I import existing business decisions before regenerating the queue, apply completed assignments, retain unresolved items and remove resolved items from the next queue. Later business changes feed a subsequent run.

Inputs and distribution

Fabric Lakehouse supplies current organisation and user data. SharePoint supplies the prior approved master and business review workbook; lookup and dashboard configuration define access attributes and distribution.

Bronze, Silver and Gold processing produces a master workbook with Group, User and Special User sheets, one new-group review workbook, 12 domain-specific dashboard workbooks and ReportRLS datasets for configured Fabric destinations. Regular-user records carry 13 business-rule-driven access attributes.

Dashboard outputs are fresh .xlsx files; generation does not run VBA or require existing macro-enabled workbooks. Monthly workbook naming does not change the daily processing cadence.

Compatibility and exceptions

Acceptance concerns approved legacy macro outputs and business rules: sheet structures, headers, column order, assignments, all 13 regular-user attributes, required blanks and dashboard mappings.

Special users retain approved exception assignments and values. They do not inherit regular organisation-group assignments or have the 13 regular-user attributes recalculated. They are appended to regular users without deduplicating by email, preserving the required legacy behavior (UNION ALL).

Employee-data boundary

Configured PII is encrypted before persistence in Databricks data. Deterministic hashes support identifier matching across protected datasets; Azure Key Vault protects encryption material. DEV and PRD use separate security configurations and key material.

Authorised export processing decrypts required PII. Excel outputs and configured Fabric destinations may contain decrypted information; logs must exclude plaintext employee data and secrets.

Production operations

ADF orchestrates separate Databricks activities. Pipeline run identifiers connect processing and structured logs. Validation covers source structure, row counts, protected joins, assignments and output schemas.

Source, permission, processing and publishing errors surface as failures. Publishing handles locked SharePoint files. Setup and deployment operations are separate from daily processing; business reviewers retain access decisions and approval.
Azure Target Architecture Central Pattana

A clearer operating model.

Progress

Target direction approved; transition preparation ongoing; publication method open. Implementation and recovery validation remain incomplete.

Objective

Address ownership, access, publication and operational-readiness gaps while retaining working controls.

Challenge

Responsibilities and controls were inconsistent across platform and organisational boundaries.

My role & scope

I assessed the platform, designed the target and aligned responsibilities and transition priorities with infrastructure and security stakeholders.

What I did

  • I assessed access, publication and operational gaps.
  • I translated findings into architecture and operating-model decisions, retaining Unity Catalog and DEV/PRD separation.
  • I am preparing the transition around aligned responsibilities and dependencies.
Current to Target

Current

CPN

Sources + ADF

Public paths

Databricks + ADLS

Daily OneLake copies

Fabric + Power BI

Target (proposed)

RIS foundation / CPN workloads

Sources + ADF

Private paths / Approved destinations

Domain workspaces / catalogs

Publication undecided

Fabric + Power BI

Separate approvals

Existing: Unity Catalog, DEV/PRD. Fabric access stays separate.

Proposed: recovery objectives, restoration tests, release approval, tested rollback.

Solid: current. Dashed: proposed.

Engineering details

Assessment basis

I assessed the platform using confirmed interview answers. The assessment is a draft with content review Pending, not an independently verified audit. Its findings shaped the target architecture and transition priorities with infrastructure and security teams.

Retained controls

Retain Unity Catalog-governed ADLS access, DEV/PRD separation, centralized secrets, production failure alerts, cost controls and unchanged DEV-tested artifact promotion. Existing account-removal and integration practices remain. Unity Catalog does not enforce Fabric access.

Assessment → design response
Assessment themeFinding → proposed response
Ownership and accessResponsibilities are undocumented and catalog owners unassigned. I proposed accountable data ownership, recorded approvals, periodic reviews and time-limited access.
Controlled connectivityPartial network restrictions informed private service paths, shared network responsibilities and approved outbound destinations, distinguishing browser access from data transfer.
Trusted publicationDaily copies lack ownership and validation. The response pairs publication ownership and consumer approval with freshness checks and source-to-copy reconciliation.
Operational readinessAlerts and artifact promotion already work. Missing recovery and release safeguards call for agreed recovery objectives, restoration testing, release approval and tested rollback.

Method

Establish the baseline, assess gaps, define the target and operating model, then sequence and validate change. This describes the method, not completion of all stages. Architecture enables improvements; implemented, tested practices demonstrate closure.

Approval and delivery boundaries

Team Head approved the target direction; individual standards require separate approval. RIS owns identity and shared foundation; CPN owns delegated platform workloads. Domain workspaces and catalog ownership remain proposed.

Current Databricks-to-OneLake publication uses daily copies over the public internet. The future publication method and connectivity remain open. Fabric consumer access requires separate approval.

Transition preparation is in progress. Migration, control closure, recovery readiness and measured risk reduction are not complete. Restoration testing and release rollback remain separate obligations.

Continue the conversation.